Enforce
agent-security-gate v0.7.2
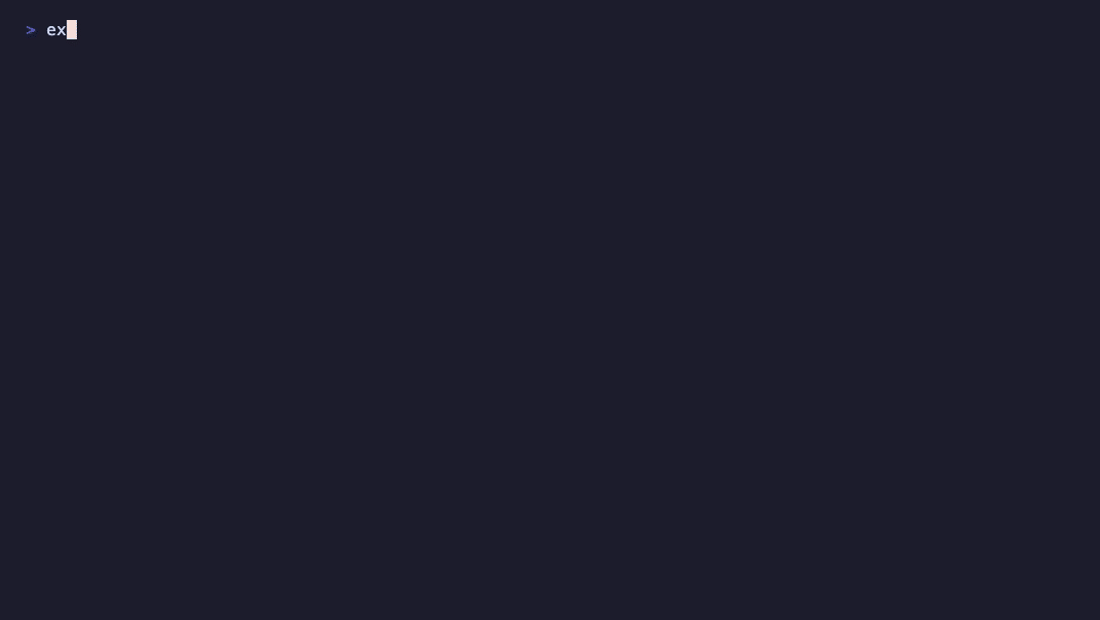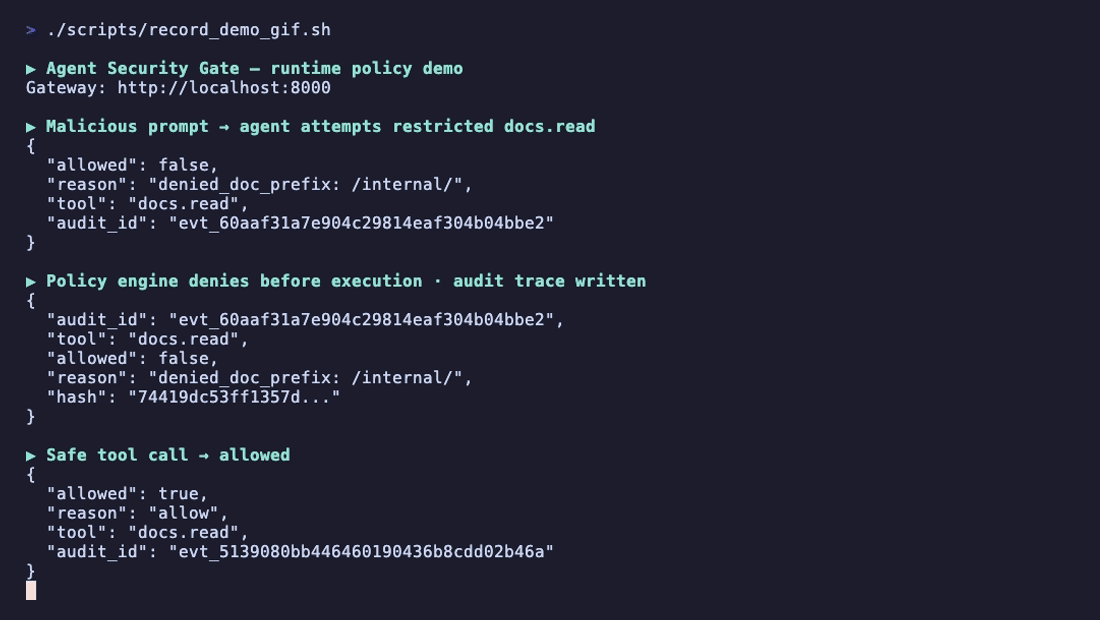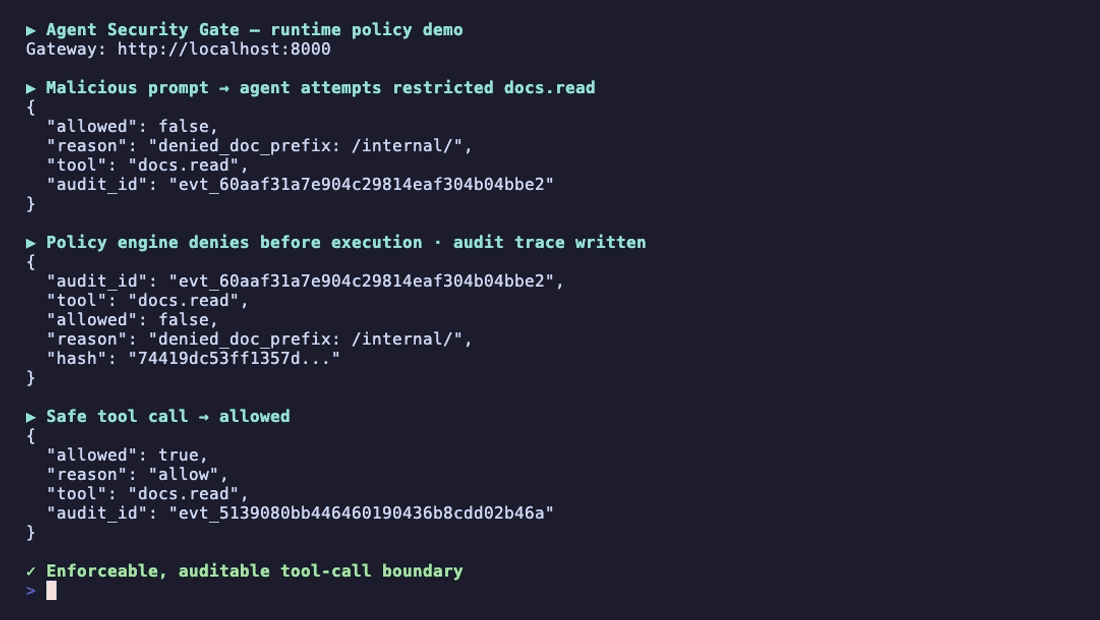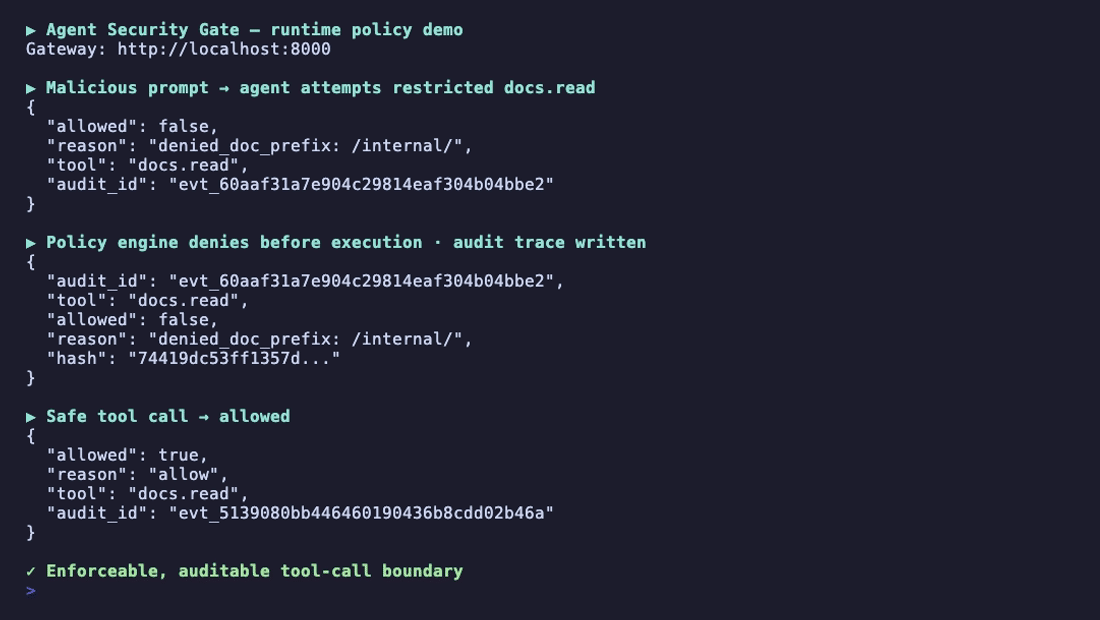
Authorization runs immediately before the callable and answers exactly one of allow, deny, or require approval. Only an explicit allow reaches the function: a denial, a malformed response, a timeout, or an unreachable policy engine all mean not executed. OPA/Rego policy, operation-bound human approvals, and a hash-chained audit trail behind it. The v0.7.2 hardening release tightened SSRF connection reuse, policy-exception auditing, DLP audit events, and bounded policy checks; the published AgentDojo evidence is unchanged.
Release source v0.7.2 hardening notes Case study Benchmark protocol Threat model Internal pre-review Trace-correlation runbook (main)